
Markus Keil
Partner, IT & Controls Assurance
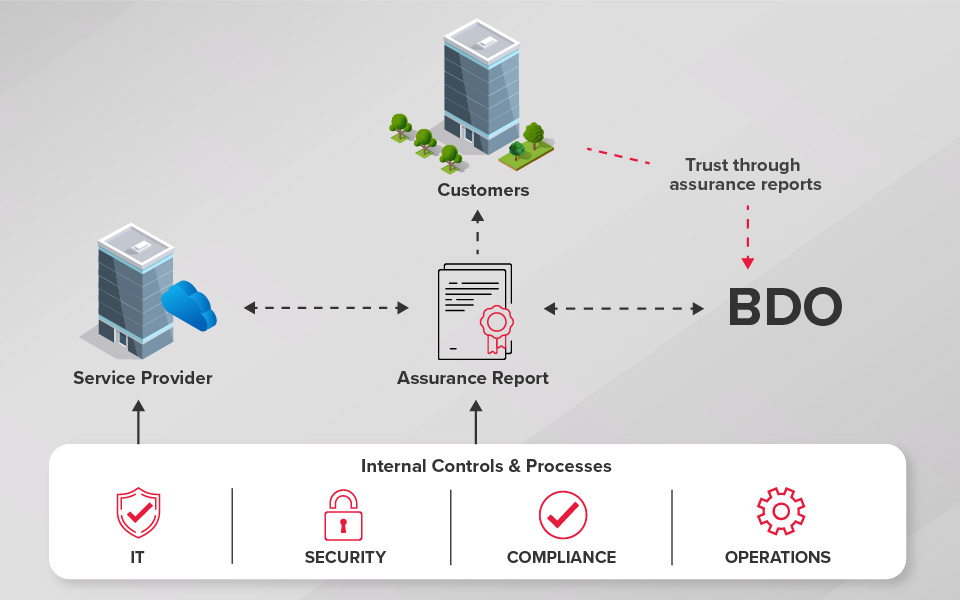
Companies are increasingly outsourcing business-critical processes and IT services to specialised service providers. At the same time, the requirements of customers, supervisory authorities and business partners regarding transparency, information security and effective internal controls are increasing. With our outsourcing assurance services, we support service providers in having the effectiveness of their control systems independently audited and demonstrably documented for their customers – in accordance with nationally recognised and internationally established assurance standards.
Outsourcing assurance is a key sub-area of third party assurance and is aimed in particular at service companies that provide outsourced processes or IT services for their customers. Third party assurance refers to independent audits that enable companies to provide reliable evidence to customers, business partners, auditors or supervisory authorities regarding defined processes, controls or infor
An independent assurance report builds trust and reduces the audit effort for your customers. Instead of individual audits, your clients receive standardised evidence of the design and – depending on the report type – also the effectiveness of your internal control system.
Outsourcing assurance supports you in:
Independent audit of your controls
Fulfilment of regulatory and contractual requirements
Fewer individual audits and greater market acceptance
The appropriate standard is not determined by the industry, but by your customers’ requirements, the subject matter of the audit and the intended recipients of the assurance report. We are happy to support you in selecting the assurance standard that is suitable for your company or in combining several reports.
Many companies today require several assurance reports at the same time. This is particularly relevant in the context of third party assurance and multi regulatory compliance, when companies must simultaneously meet the requirements of different regulatory provisions and standards. Instead of having the same controls audited multiple times, a shared control framework enables the efficient execution of combined audits. This significantly reduces documentation effort, interviews and audit time.
| Your starting point | Typical audit subject matter | Commonly suitable report | Typical recipients |
| Your service affects your customers’ financial reporting | Financially relevant business processes and controls | IDW PS 951 revised version, ISAE 3402 or SOC 1 | Customers, their management and auditors |
| International or US-oriented customers require an ICFR-related report | Controls relevant to internal control over financial reporting | SOC 1 or ISAE 3402, depending on the required framework | International customers and their auditors |
| Customers require evidence of security and digital services | Security, availability, confidentiality, privacy or processing integrity | SOC 2 | Customers, auditors, due diligence and procurement teams |
| You want to publicly communicate a successful SOC 2 audit based on the TSC criteria | Concise evidence without confidential control details | SOC 3 | Prospects, the public and sales teams |
| You offer cloud services in the German market | Cloud-specific security and transparency criteria | BSI C5 | German customers, public-sector clients and regulated companies |
| The audit subject matter is outside financial reporting | Individual compliance, information or control requirements | ISAE 3000 | Depending on the engagement and the defined criteria |
Evidence of an appropriate internal control system for outsourced services in the German market.
Internationally recognised assurance standard for services that affect financial reporting.
Report for international customers on controls relevant to internal control over financial reporting (ICFR).
Evidence of information security, availability, integrity, confidentiality and privacy based on the Trust Services Criteria.
Publicly available report based on a successful SOC 2 assessment.
Flexible assurance standard for assurance engagements outside financial reporting.
Audit of cloud services in accordance with the BSI Cloud Computing Compliance Criteria Catalogue.
Together, we define the relevant standards, control areas and audit scope – including multi-regulatory mapping.
We analyse the current maturity level of your control system, identify deviations from the requirements of the selected standard and derive specific recommendations for closing the identified gaps.
In the readiness assessment, we evaluate whether your processes, controls and evidence are sufficiently prepared for a successful assurance audit and identify optimisation potential before the actual audit begins.
We audit the design and operating effectiveness of the controls in accordance with the selected standards – efficiently and transparently.
You receive a reliable assurance report, optionally as a multi-standard report.
We support you in further developing your control system and in future audit cycles.
Experience with national and international service providers across various industries.
Audit, readiness assessment, gap analyses and combined assurance services from a single source.
Auditors, IT auditors, information security experts and internal control system specialists work closely together.
Use of shared control frameworks and integrated audits to reduce overall effort.

We support you with a holistic audit and advisory approach that combines regulatory compliance, operational efficiency and technological future readiness. Our interdisciplinary teams bring together expertise in audit, IT & controls assurance, information security and compliance. This results in integrated solutions tailored to your specific requirements as a service provider – from selecting the appropriate standard, readiness assessments and gap analyses through to the efficient execution of combined assurance audits. As one of the world’s leading audit and advisory firms, we support you with many years of experience, deep industry knowledge and a clear focus on scalable, future-ready control systems.