Because a Privacy Information Management System Makes Data Protection Auditable
Today, companies process personal data across numerous processes, systems, entities and external service providers. This increases the requirements for protecting data and, consequently, for a transparent, consistent and auditable data protection organisation. Companies therefore face the task of incorporating existing data protection measures into a structured management system and clearly defining roles, responsible parties and interfaces. They also need to systematically identify and address data protection and security risks, establish measurable objectives and put appropriate evidence in place. At the same time, they need to integrate the requirements of ISO/IEC 27701:2025 into existing processes, align data protection with information security, compliance, risk management and other management systems, and prepare the organisation for internal audits and potential certification.
Systematically Developing Data Protection Management
A Privacy Information Management System (PIMS) in accordance with ISO/IEC 27701:2025 helps companies embed data protection requirements within their organisation in a structured and lasting manner. The ISO 27701 standard provides a structured framework with a defined scope, clear roles, measurable objectives, risk treatment, and regular audits and management reviews. At the same time, it improves the ability to demonstrate the measures in place and links data protection with existing management and governance structures.
As a standalone privacy information management system standard, ISO/IEC 27701:2025 can be implemented and certified independently of ISO/IEC 27001, with a stronger focus on governance, data protection risks and continual improvement. This creates auditable, future-ready data protection management for companies of all sizes. For example, customers’ personal data can be processed in compliance with applicable requirements and statutory security provisions. Structured ISO 27701 advisory services help determine the specific action required, assess existing structures through a gap analysis, and define the next steps for PIMS implementation, audit readiness and certification preparation.
Our services at a glance
1. Current State Assessment & Gap Analysis
BDO analyses the existing data protection organisation and relevant interfaces and compares them against the requirements of the ISO 27701 standard. We assess which structures and measures are already in place and which areas still require action.
On this basis, we assess the current maturity level and develop a prioritised roadmap for the areas requiring action. This gives companies a clear picture of their starting point, the measures required and the next steps towards an effective PIMS.
2. Design & PIMS Implementation
Building on the gap analysis, BDO supports the design and implementation of the PIMS. This includes defining the context, content and scope, roles and reporting lines, as well as developing a data protection policy, objectives, risk methodology and the required PIMS documentation. Wherever possible, appropriate measures and evidence are integrated into existing processes and management structures. The result is a PIMS tailored to the organisation that builds on existing structures and systematically addresses the requirements of the ISO 27701 standard.
3. Integration & Audit Readiness
In the next step, BDO helps integrate the PIMS into existing management and governance structures and prepare the organisation for internal audits and management reviews. A readiness assessment identifies which requirements have already been met and which outstanding issues should still be addressed before an external audit. This forms the basis for a structured action plan that supports further certification preparation and embeds continual improvement of the PIMS.
This gives companies a clear understanding of which measures should still be implemented before an external audit and how they can take a structured approach to achieving audit readiness and preparing for certification.
Our Approach to ISO/IEC 27701 Readiness
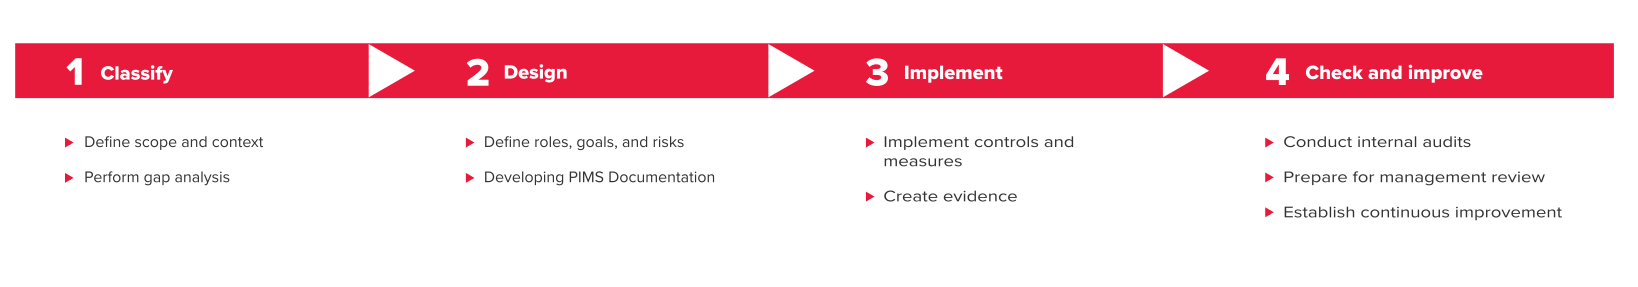 From the initial current state assessment through PIMS implementation to audit readiness, BDO provides structured support to companies on their path towards an effective and auditable Privacy Information Management System.
What Happens After Audit Readiness?
Once the organisation is prepared for certification, the next step is the external certification process conducted by an independent certification body such as TÜV Nord or TÜV Süd. This assesses whether the implemented PIMS meets the requirements of the ISO 27701 standard and whether compliance is effectively achieved within the organisation. BDO supports companies in preparing for this step, addressing identified areas for action, and preparing the required evidence and data in a structured manner. The certification audit itself and the decision on certification are carried out by the independent certification body. This ensures a clear division of roles: BDO provides support from the current state assessment through PIMS implementation to certification readiness, while the external audit and certification are conducted independently.
Your benefits with BDO
- Interdisciplinary expertise:
Combining data protection, IT, cyber security, compliance and audit expertise - Modular approach:
From a compact maturity assessment to comprehensive implementation support - Audit-oriented perspective:
A focus on clear, traceable documentation, effective controls and robust evidence - Practical implementation:
Recommendations aligned with existing processes, standards, risks and resources - Integration rather than a standalone solution:
Existing management and governance structures can be leveraged and further developed in a targeted manner
Our 360° approach

BDO combines interdisciplinary expertise in data protection, information security, compliance, risk management and auditing. With a holistic 360° approach, we help companies embed data protection in a systematic, transparent and future-ready way. We always take our clients’ perspective and consider existing processes and governance structures. As one of the leading audit and advisory firms, we are a reliable partner for all your questions and work with you to find practical, flexible solutions that combine regulatory certainty with efficiency.
FAQ